Blocking Clients via Cookies
If you can identify abusive clients from within your application, you can block those clients by setting a cookie that you defined as a blocking rule:
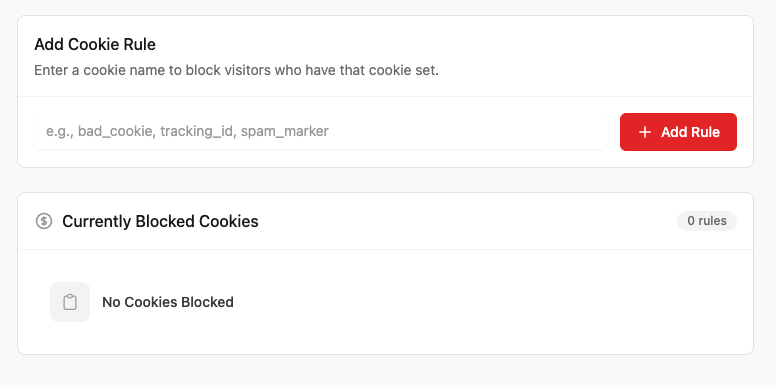
Available on the Advanced, Professional, Network, and Enterprise plans.
How Cookie Rules Match
Each rule is a piece of text. Expedited WAF blocks a request when that
text appears anywhere in the request’s Cookie header, in a cookie
name or in a cookie value. The match is case-sensitive.
For a rule of PHPSESSID:
PHPSESSID=abc123is blocked (cookie name)theme=dark; PHPSESSID=abc123is blocked (one of several cookies)MYPHPSESSID2=abc123is blocked (the text is part of a longer name)flag=PHPSESSIDis blocked (the text is in a value)phpsessid=abc123is not blocked (different case)
Because values are matched too, you can block on a value your
application sets, such as flag=banned. Choose text that won’t appear
in your legitimate visitors’ cookies: a short or common rule can block
real users. To cover different capitalizations, add a rule for each
one.